Capabilities, Limitations, BYOK & CI/CD
Honest What is There vs. What is Not matrix, BYOK privacy lifecycle (Gemini, OpenAI, Anthropic), Zero-Secret S3/Azure SAS cloud workspaces, and GitHub Actions SARIF pipelines.
“Zero-secret architecture means you never have to trust our server with your LLM keys or cloud storage tokens.”
1. Honest Comparison Matrix: What's Built-In vs. Known Boundaries
NodeMotion is designed for principal engineers, security architects, and compliance reviewers who require complete clarity on how deterministic vs. AI-assisted features operate:
- Deterministic <5ms STRIDE + MITRE ATLAS Engine: 100% browser-executed graph evaluation across Spoofing, Tampering, Repudiation, Info Disclosure, DoS, Elevation of Privilege, and Agentic AI (
NM-ATLAS-LLM01). - Dual-Engine IaC & GitHub Ingestion: Serverless AI extraction (
/api/parse-iac) paired with an instant offline deterministic HCL/Bicep/Compose/K8s/OpenAPI parser. - 1-Click Architectural Auto-Fixes & Control-Break Simulator: Mutates live DFD topology to splice Cloud WAFs, attach SIEM collectors, inject AI Safety Guardrails, upgrade edges to
mTLS 1.3, or simulate control failures (NM-STRIDE-E02). - 5 Security Exports + 7 Architecture Exports: OASIS SARIF v2.1.0, OWASP Threat Dragon v2, Jira CSV, CISO PDF, DOCX/PDF Runbooks, Animated SVG, Mermaid, PlantUML, and
.nodemotion.json.
- Not an Application Source-Code SAST/DAST Scanner: NodeMotion threat-models architectural Data Flow Diagrams and IaC definitions—it complements (rather than replaces) CodeQL, Semgrep, or Snyk for line-by-line C#/Python/Go vulnerabilities.
- No Dynamic Terraform State Execution: The deterministic HCL fallback parses resource blocks and attributes statically without running
terraform planagainst live cloud credentials. - Public GitHub Repos for Direct Browser Tree Fetch: Direct browser tree discovery calls
api.github.com(60 req/hr unauthenticated limit). For private repos, upload.tf/.bicepfiles via the File Upload tab.
2. Bring Your Own Key (BYOK) & Zero-Secret Privacy Architecture
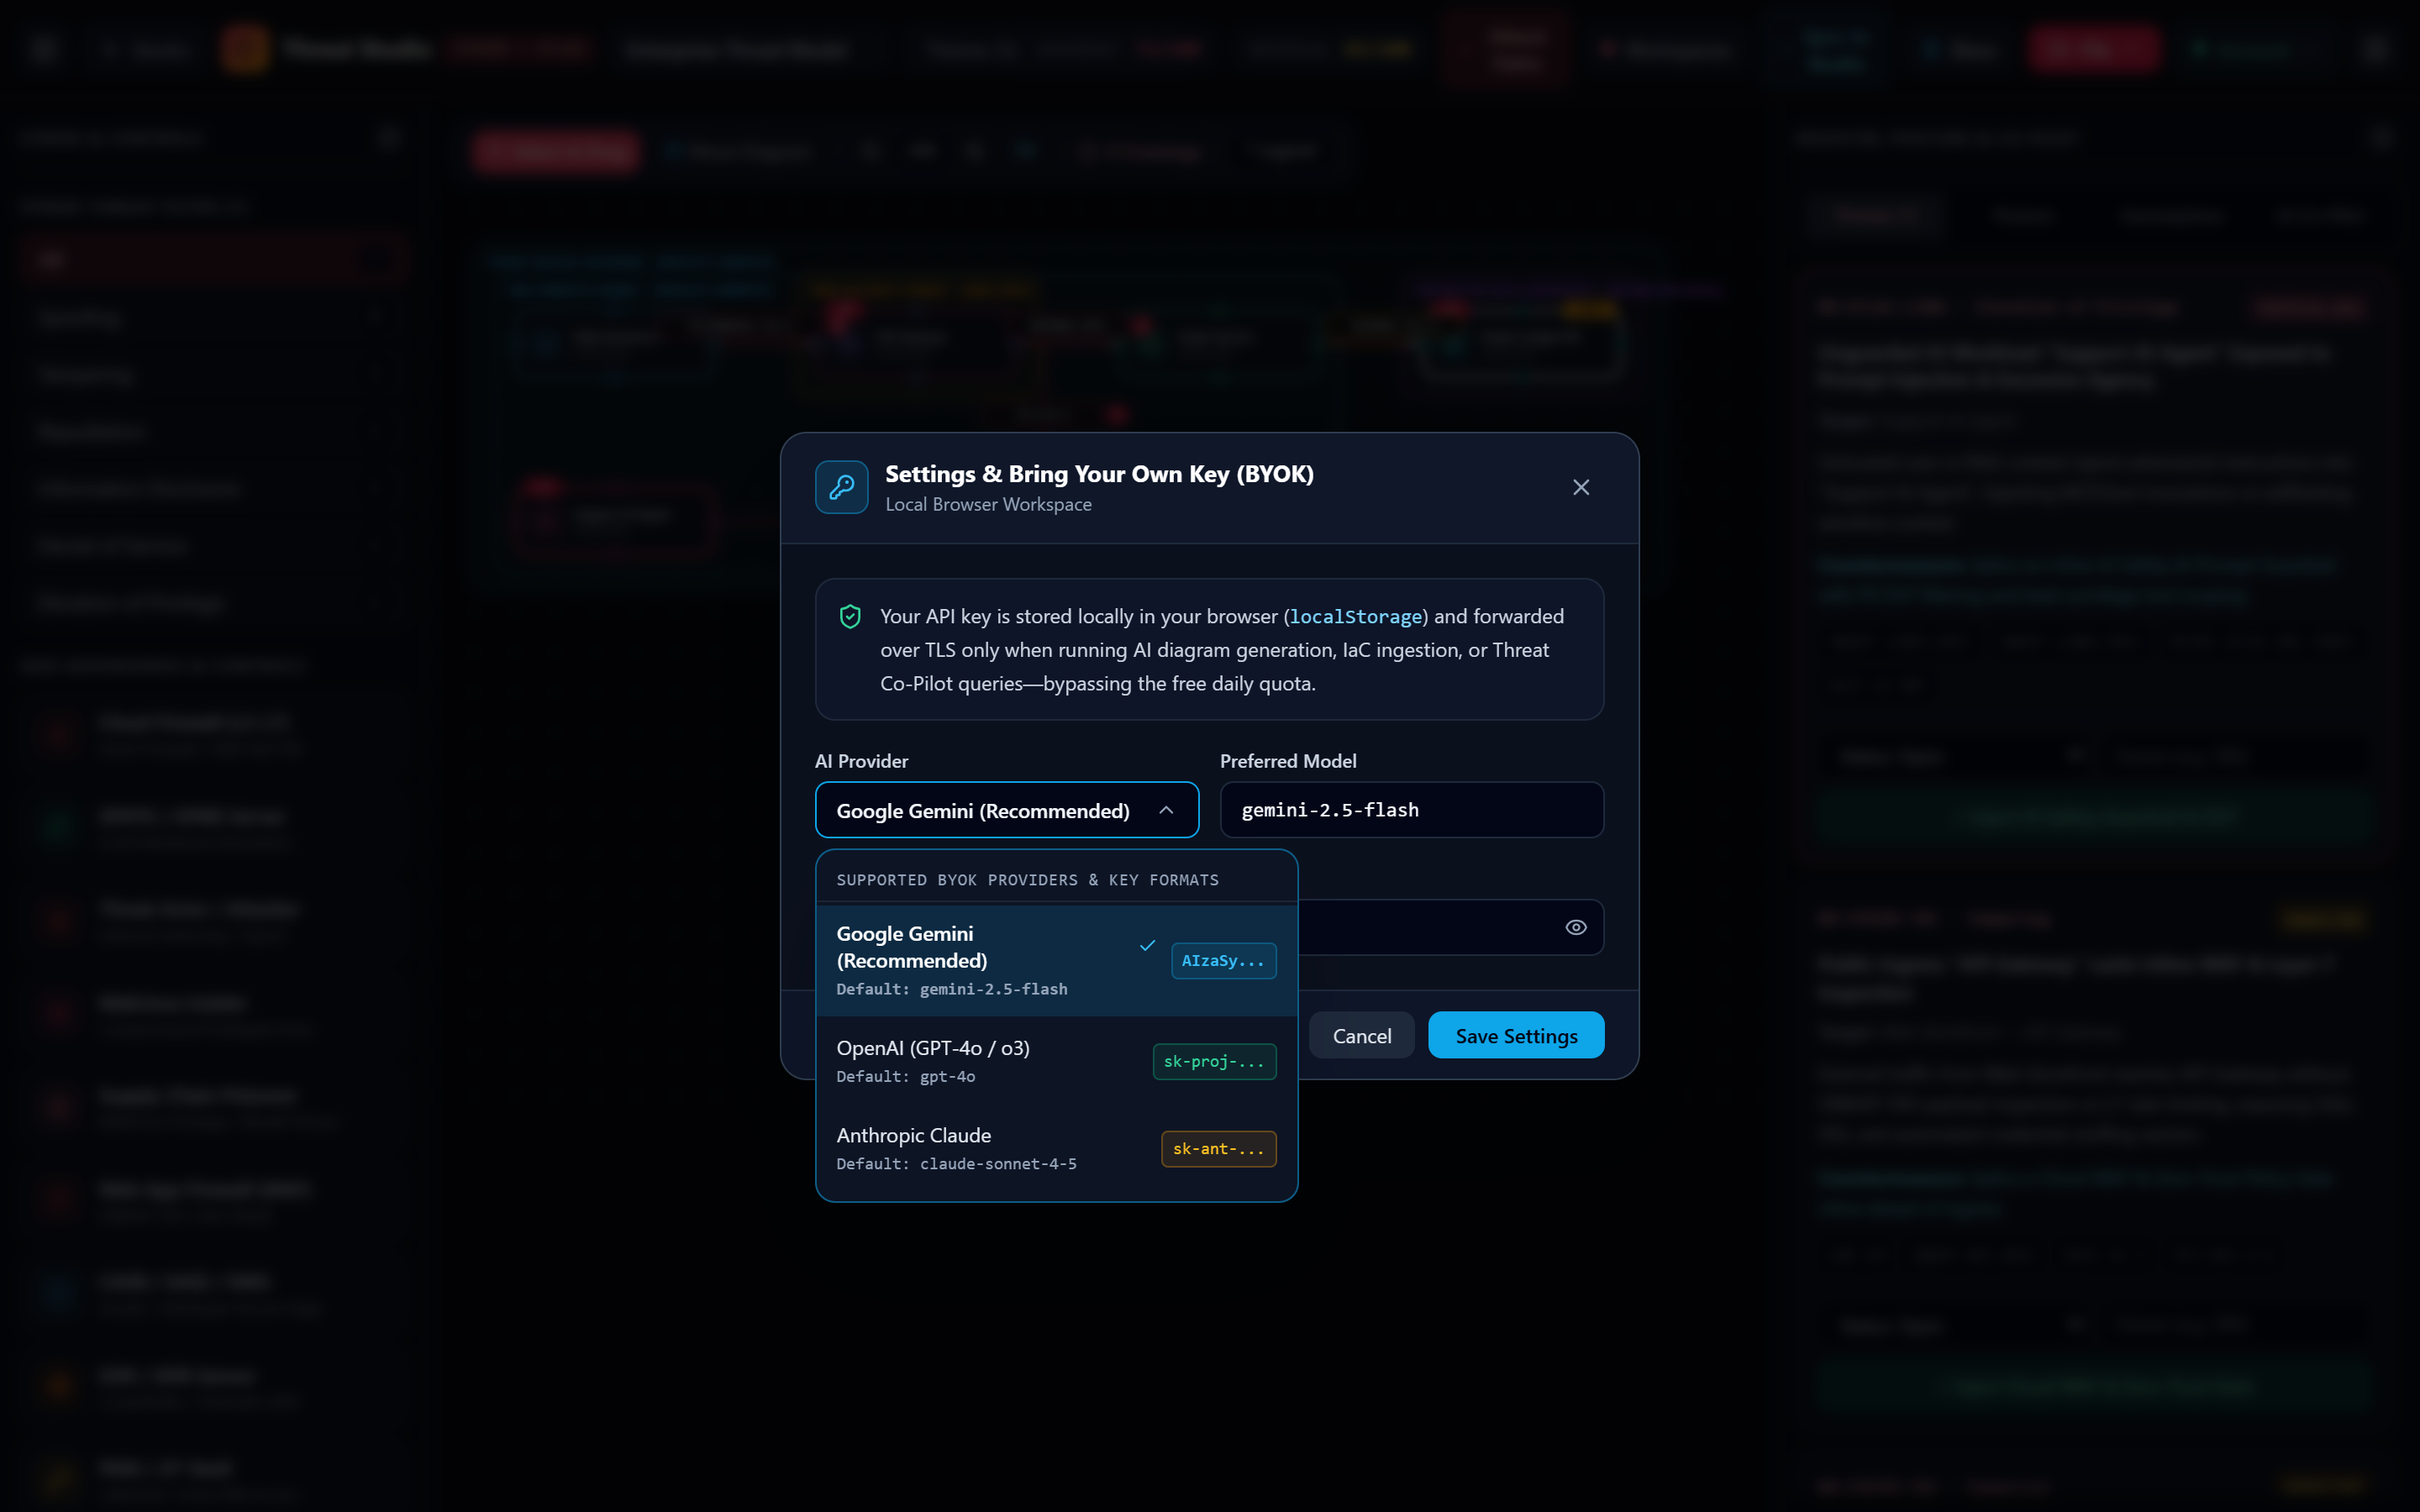
Clicking Account → Settings in either Architecture Studio or Threat Modeling Studio opens the Settings & Bring Your Own Key (BYOK) Modal, allowing you to bypass the default starter quota using your own API key from Google Gemini, OpenAI, or Anthropic Claude:
| Security Layer | Implementation Mechanism | Privacy & Compliance Guarantee |
|---|---|---|
| BYOK Local Isolation | localStorage['nodemotion_byok_config_v1'] | Your personal API key is stored strictly in your browser's localStorage and forwarded over TLS 1.3 only during active AI requests—never written to Azure Table Storage or server logs. |
| Zero-Secret Cloud Uploads | saveToPreSignedOrSasUrl() | Uploads exported diagrams/runbooks directly to your AWS S3 Pre-Signed URL or Azure Blob SAS URL over HTTPS. Optional /api/storage-relay blocks internal RFC1918 IP ranges against SSRF. |
| OWASP Edge Hardening | staticwebapp.config.json | Enforces strict Content-Security-Policy, Strict-Transport-Security, X-Frame-Options: DENY, X-Content-Type-Options: nosniff, and locked-down Permissions-Policy. |
3. CI/CD DevSecOps Pipelines: GitHub Actions & Azure DevOps SARIF Upload
Export your threat model as OASIS SARIF v2.1.0 (security/nodemotion-threat-model.sarif.json) and integrate it directly into your repository's automated security gates:
name: Upload NodeMotion SARIF v2.1.0
on:
  push:
    branches: [ main ]
    paths: [ 'security/**.sarif.json' ]
  pull_request:
    branches: [ main ]

permissions:
  contents: read
  security-events: write

jobs:
  upload-sarif:
    runs-on: ubuntu-latest
    steps:
      - uses: actions/checkout@v4
      - name: Upload STRIDE + ATLAS SARIF
        uses: github/codeql-action/upload-sarif@v3
        with:
          sarif_file: security/nodemotion-threat-model.sarif.json
category: nodemotion-architectural-stridetrigger:
branches:
include: [ main ]
paths:
include: [ 'security/*.sarif.json' ]
pool:
vmImage: 'ubuntu-latest'
steps:
- checkout: self
- task: AdvancedSecurity-Publish@1
displayName: 'Publish NodeMotion STRIDE SARIF'
inputs:
SarifsInputDirectory: '$(Build.SourcesDirectory)/security'There Are No Dumb Questions
Candid answers to the skeptical questions every security engineer asks first.
- ▸Every diagram node, edge, and trust boundary stays synchronized across studios.
- ▸1-click countermeasures update both the visual topology and Residual Risk score.
- ▸Export SARIF v2.1.0, Threat Dragon v2 JSON, Jira CSV, and CISO PDFs anytime.